How to Generate OpenVPN OVPN Files a Step by Step Guide: A Complete, SEO-Optimized Tutorial for VPN Beginners and Pros
How to generate openvpn ovpn files a step by step guide: identify, configure, and deploy your own OpenVPN client profiles with a clear, repeatable process. Quick fact: OpenVPN config files .ovpn are the portable way to store all the necessary settings for a VPN connection in one file. In this guide, you’ll get a step-by-step workflow, practical tips, and ready-to-use commands to create, sign, and distribute your OVPN profiles. We’ll cover both server-side and client-side steps, common pitfalls, and best practices so you can stay secure and connected.
What you’ll learn in this guide
- How OpenVPN works at a high level and why OVPN files matter
- A practical, repeatable step-by-step process to generate OVPN files
- How to automate certificate creation and distribution
- Common mistakes and how to avoid them
- Security best practices, including certificate revocation and rotation
- Quick reference commands, sample configs, and troubleshooting tips
Useful resources and references un clickable text
- OpenVPN official documentation - openvpn.net
- OpenSSL project - openssl.org
- Linux server administration basics - linux.org
- VPN security best practices - csoonline.com
- Certificate Authority best practices - ca.org
- How to set up a small home VPN - wiki.centos.org
- WireGuard vs OpenVPN comparison - arstechnica.com
- SSL/TLS essentials - mbed TLS blog
- Router VPN setup guides - routerguide.example
- Threat modeling for VPNs - security.stackexchange.com
Understanding the basics
- What is an OVPN file? An OVPN file is a text file that contains the VPN protocol, server address, port, and embedded certificates or keys. It may also include inline CA certificates, client certificates, and TLS auth keys.
- Why generate your own OVPN files? Custom OVPN files let you tailor security settings, manage user access, and simplify distribution to individual clients laptops, phones, etc..
Prerequisites
- A server with OpenVPN installed Ubuntu 22.04+, Debian, or similar
- EasyRSA or OpenVPN’s built-in scripts for PKI Public Key Infrastructure
- Administrative access sudo on the server
- A client device Windows, macOS, Linux, iOS, Android
- Basic familiarity with terminal/SSH
Section: Setting up the OpenVPN server Step 1 to Step 6 Step 1: Install OpenVPN and EasyRSA
- On Debian/Ubuntu:
- sudo apt update
- sudo apt install -y openvpn easy-rsa
- On CentOS/RHEL:
- sudo yum install -y epel-release
- sudo yum install -y openvpn easy-rsa
Step 2: Create the PKI infrastructure
- Make a working directory:
- make-cadir ~/openvpn-ca
- cd ~/openvpn-ca
- Initialize the PKI:
- ./easyrsa init-pki
- Build the CA you’ll be prompted to set a passphrase and common name:
- ./easyrsa build-ca nopass
- If you want a password, omit nopass and keep it secure
Step 3: Generate server certificate and key
- Build server certificate and key:
- ./easyrsa build-server-full server nopass
- Generate TLS-Auth key optional for extra security:
- openvpn --genkey --secret ta.key
Step 4: Generate client certificates
- For a specific client e.g., user1:
- ./easyrsa build-client-full user1 nopass
- You can repeat for more clients as needed
Step 5: Generate Diffie-Hellman parameters
- OpenVPN requires Diffie-Hellman:
- ./easyrsa gen-dh
Step 6: Prepare the server config
- Copy the example server config and tailor it:
- gunzip -c /usr/share/doc/openvpn/examples/sample-config-files/server.conf.gz > /etc/openvpn/server.conf
- Edit /etc/openvpn/server.conf:
- set port 1194
- set proto udp
- push "redirect-gateway def1 bypass-dhcp"
- push "dhcp-option DNS 1.1.1.1"
- set cert and key paths to the generated files
- set ca to the CA certificate path
- set TLS-auth ta.key if you generated it
Step 7: Move the keys and certificates into /etc/openvpn
- sudo cp ~/openvpn-ca/pki/ca.crt /etc/openvpn/
- sudo cp ~/openvpn-ca/pki/issued/server.crt /etc/openvpn/
- sudo cp ~/openvpn-ca/pki/private/server.key /etc/openvpn/
- sudo cp ~/openvpn-ca/pki/dh.pem /etc/openvpn/dh.pem
- sudo cp ~/openvpn-ca/ta.key /etc/openvpn/
Section: Creating client OVPN files Step 7 and beyond Step 8: Create a standard client configuration template
- Start with a baseline client.conf:
- client
- dev tun
- proto udp
- remote YOUR_SERVER_IP 1194
- resolv-retry infinite
- nobind
- persist-key
- persist-tun
- remote-cert-tls server
- cipher AES-256-CBC
- verb 3
- Optional: TLS-auth
Step 9: Embed certificates in the client file inline mode
- Retrieve client certificates:
- cat pki/ca.crt
- cat pki/issued/user1.crt
- cat pki/private/user1.key
- Assemble the OVPN with embedded data:
...ca.crt contents... ...user1.crt contents... ...user1.key contents... - If using ta.key for TLS-auth, embed as:
... ta.key contents ... with key-direction 1 or 0 in the config
Step 10: Create the final .ovpn file
- Put the server address, port, and embedded blocks into a single file:
- client
- dev tun
- proto udp
- remote YOUR_SERVER_IP 1194
- resolv-retry infinite
- nobind
- persist-key
- persist-tun
- remote-cert-tls server
- cipher AES-256-CBC
...contents... ...contents... ...contents... ...contents... if used- key-direction 1 for tls-auth
Step 11: Transfer the .ovpn file to clients securely
- Use a secure file transfer method: scp, SFTP, or a secure portal
- For mobile devices, you can email a link or use a cloud-based secure file share with expiration
Section: Automation and best practices Automation tips
- Script the entire flow: generate-ca, create-client, embed certs, and output .ovpn
- Use a Makefile or bash script to standardize the process
- Keep a registry of issued client certificates and revoke as needed
Certificate management
- Revocation: Maintain a revocation list CRL and publish it if you’re doing larger deployments
- Rotation: For security, rotate keys and certificates every 12–24 months, or after a suspected breach
- Certificate naming: Use a strict naming convention e.g., client-country-YYYYMMDD
Security hardening tips
- Use TLS-auth ta.key and set key-direction in client config
- Use a strong cipher AES-256-CBC and TLS version minimum TLS 1.2 or higher
- Prefer UDP for better performance but have TCP as a fallback if needed
- Disable client-to-client in server config if you don’t need inter-client communication
- Enable automatic restart on server changes with systemd
Format options for distribution
- Inline vs. separate certs:
- Inline OVPN files are convenient for end users
- Separate certs can make revocation and rotation easier in larger deployments
- Packaging:
- Create a zip or tarball per user with the OVPN file and a quick setup guide
- Provide a single global config for mass distribution and individual customized OVPNs for large teams
Troubleshooting quick checks
- Check server status: sudo systemctl status openvpn@server
- Verify that the firewall allows UDP 1194
- Confirm IP forwarding is enabled:
- sudo sysctl -w net.ipv4.ip_forward=1
- echo "net.ipv4.ip_forward=1" | sudo tee -a /etc/sysctl.d/99-forwarding.conf
- Review logs for clues:
- journalctl -u openvpn@server -e
- tail -f /var/log/openvpn.log
Format: tables and lists for quick reference Common file layout
- Server files:
- /etc/openvpn/server.conf
- /etc/openvpn/ca.crt
- /etc/openvpn/server.crt
- /etc/openvpn/server.key
- /etc/openvpn/dh.pem
- /etc/openvpn/ta.key optional
- Client files:
- client1.ovpn inline or separate your certs
- client1.crt
- client1.key
- ca.crt
- ta.key optional
Sample inline OVPN file snippet
- client
- dev tun
- proto udp
- remote vpn.example.com 1194
- resolv-retry infinite
- nobind
- persist-key
- persist-tun
- remote-cert-tls server
- cipher AES-256-CBC
- -----BEGIN CERTIFICATE-----
- MIIBIjANB... example
- -----END CERTIFICATE-----
- -----BEGIN CERTIFICATE-----
- MIIBOjCCA... example
- -----END CERTIFICATE-----
- -----BEGIN PRIVATE KEY-----
- MIIEvQIBADANB... example
- -----END PRIVATE KEY-----
- -----BEGIN OpenVPN Static key
- 60f5d2a... example
- -----END OpenVPN Static key
- key-direction 1
Performance considerations
- Server capacity: 1–2 MB per user per hour for typical streaming usage; plan capacity accordingly
- Simultaneous connections: Start with 5–10 and scale up as needed
- Bandwidth planning: Ensure your uplink can handle the aggregate client demand
Troubleshooting common client issues
- “TLS key negotiation failed”: Check ta.key existence and correct embedding in the OVPN file
- “Cannot allocate TUN/TAP dev dynamically”: Ensure TUN module is enabled on the server and the user has permissions
- “AUTH: Received control message: AUTH_FAILED”: Verify credentials and CA certificate match
- “VPN connection drops frequently”: Consider increasing keepalive and ping timing in server and client configs
Modern alternatives and comparisons
- OpenVPN vs WireGuard: OpenVPN offers mature features and compatibility; WireGuard is faster but newer and sometimes less feature-rich
- When to choose TLS-auth vs TLS-crypt: TLS-auth offers extra protection against certain attacks; TLS-crypt encrypts control channel and data
Scaling to teams and enterprises
- Centralized certificate management: Use an automated CA and a connection portal to issue terminal-specific OVPN files
- Logging and monitoring: Centralize logs from OpenVPN servers and set up alerting for unusual connection patterns
- Compliance: Align with organizational policies for data privacy and encryption standards
Frequently asked questions
What is an OVPN file?
An OVPN file is a single configuration file that includes all necessary settings, certificates, and keys to establish a VPN connection with an OpenVPN server.
Can I embed certificates directly into the OVPN file?
Yes. Embedding certificates inline simplifies distribution, but ensure you protect the file with secure access.
Do I need TLS-auth for my OpenVPN setup?
TLS-auth adds an extra HMAC protection layer to the TLS handshake. It’s recommended for extra security, especially in exposed networks.
How do I revoke a VPN certificate?
Use your PKI management tool EasyRSA to revoke the certificate and regenerate or publish a CRL as needed.
What happens if my server IP changes?
Update the remote line in each OVPN file to reflect the new server IP or domain and redistribute the updated files to clients. How to Install and Use Urban VPN Chrome Extension for Basic IP Masking: A Simple Guide to Quick, Secure Browsing
Is OpenVPN compatible with mobile devices?
Yes, many mobile apps support OpenVPN and can import OVPN files directly.
Should I host OpenVPN on UDP or TCP?
UDP is generally faster and preferred for VPNs; TCP can be used as a fallback for networks that block UDP.
How can I automate OVPN file generation?
Create scripts that automate certificate creation, file embedding, and output of a ready-to-use .ovpn file for each client.
How often should I rotate certificates?
Regular rotation is a good security practice—typically every 12–24 months or after any security incident.
How can I securely distribute OVPN files to users?
Use a secure portal, encrypted email with expiration, or an enterprise app that enforces access controls and auditing. Nordvpn Extension for Edge Your Quick Guide to Download Install and Use: Quick Start, Tips, and Pro Tricks
Additional tips and final notes If you’re setting up a VPN for the first time, take it slow and document each step. A well-documented process not only speeds up onboarding for new teammates but also helps you audit and troubleshoot later. And if you’re looking to simplify the experience for users, consider offering a simple “one-click import” where your .ovpn file is pre-stored in a secure download link with a short expiration.
Affiliate note For extra privacy and security during setup, you might consider using a trusted VPN service to test your OVPN configurations and ensure your own server is correctly hardened. If you’re curious, you can check out NordVPN for additional comparison and testing scenarios via this link: NordVPN
Frequently Asked Questions
- Is it necessary to use EasyRSA for PKI?
- Can I generate OVPN files on Windows, macOS, or Linux?
- How do I debug a failed OpenVPN connection?
- What are the security risks of embedding certificates?
- How can I prevent hijacking of VPN credentials?
- Are there legal considerations for running a VPN?
- Can I use OpenVPN with a commercial certificate authority?
- What are the best practices for logging and monitoring?
- How do I handle certificate expiration securely?
- Can I deploy VPNs at scale for a classroom or small business?
| VPN | Obfuscation | From / month | Plan | Free plan | Refund | Alipay | UnionPay | Crypto | Website opens in China | Trustpilot | |
|---|---|---|---|---|---|---|---|---|---|---|---|
 NordVPN | Turn on manually Obfuscated Servers / NordWhisper | $3.49/mo | 27 months: $94.23 | No | 30 days | ? | ✗ | ✓ | ✓ | ✗ Blocked | 4.2/5 (51,628 reviews) |
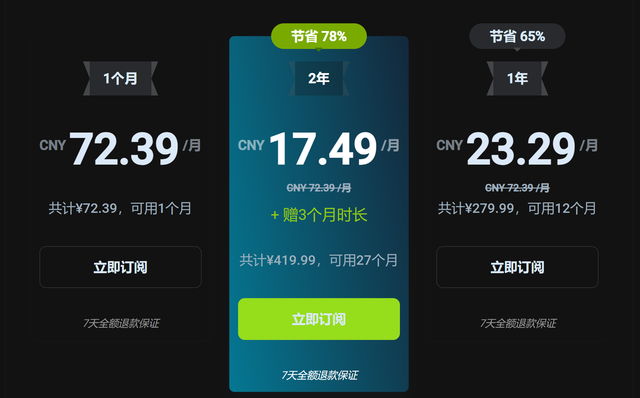
 ZoogVPN | Turn on manually Shadow | $2.49/mo | 27 months: $59.99 | Yes | 7 days | ✓ | ✓ | ✓ | ✓ | Official site blocked; our special link opens (4.4 s) | 4.2/5 (195 reviews) |
 ExpressVPN | ✓ On by default all servers | $3.00/mo | 28 months: $84 | No | 30 days | ✗ | ✗ | ✓ | ✗ | ✗ Blocked | 4.4/5 (29,706 reviews) |
 Surfshark | ✓ On by default Camouflage, with OpenVPN | See site | See site | No | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.3/5 (31,823 reviews) |
 Proton VPN | Turn on manually Stealth, free plan too | $2.99/mo | 12 months: $35.88 | Yes | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 2.1/5 (1,040 reviews) |
 Astrill VPN | Turn on manually StealthVPN / OpenWeb | $12.50/mo | 24 months: $300 | No | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 1.3/5 (110 reviews) |
 Private Internet Access | Turn on manually Shadowsocks, OpenVPN only | $2.03/mo | 40 months: $81.2 | No | 30 days | ✗ | ✗ | ✗ | ✗ | ✗ Blocked | 4.2/5 (11,033 reviews) |
 CyberGhost | Turn on manually selected servers | $2.19/mo | 28 months: $61.32 | No | 45 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.0/5 (24,178 reviews) |
 PureVPN | Turn on manually switch to OpenVPN | $1.69/mo | 60 months: $101.55 | No | 31 days | ? | ? | ✗ | ✓ | ✗ Blocked | 4.4/5 (17,994 reviews) |
 AdGuard VPN | ✓ On by default TrustTunnel | $2.99/mo | 24 months: $71.76 | Yes | 30 days | ✓ | ✗ | ✓ | ✓ | Official site blocked; our special link opens (3.7 s) | 4.3/5 (290 reviews) |
 Mullvad | Turn on manually QUIC / Shadowsocks / LWO | $5.61/mo | €5/mo | No | 14 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 3.2/5 (192 reviews) |
 Windscribe | Turn on manually Stealth / WStunnel | $5.75/mo | 12 months: $69 | Yes | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.7/5 (13,355 reviews) |
 StrongVPN | Turn on manually Scramble, OpenVPN TCP | See site | See site | No | 30 days | ✓ | ✗ | ✗ | ✗ | ✗ Blocked | 4.4/5 (2,695 reviews) |
 LightXtreme 闪连 | Not listed | $7.08/mo | 12 months: $84.99 | Yes | 30 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (3.5 s) | No page |
Prices checked 2026-11-10 on each vendor's pricing page (cheapest long plan, USD). Check the vendor's checkout for the final price.
Obfuscation checked 2026-11-14 on each vendor's site and help center: "on by default" = nothing to set; "turn on manually" = switch protocol or mode in settings; "not listed" = the vendor describes no obfuscation.
Payment methods checked 2026-11-10 on each vendor's payment pages: all 14 take cards and PayPal; ✗ = not listed, ? = the vendor's own pages disagree.
China access: whether the official website opens from mainland China networks (tests the website only, not the VPN connection). Last checked 2026-11-18 01:02 Beijing time.
Trustpilot score and review count checked 2026-11-10.